
Measure Risk
Turn varied assurance evidence into a standardized, comparable measure of information risk across an entire third-party portfolio.
Information Risk
IRIDX enables standardized measurement of third-party information risk and exposure for precise management and governance.
IRIDX
Organizations have more assurance sources than ever, but lack a consistent way to express how much risk exists with a vendor. IRIDX brings measurement discipline to that gap.
The result is more than a faster review. It is a measurement foundation for deciding how to manage and govern third-party risk across an entire portfolio.
Brand explainer
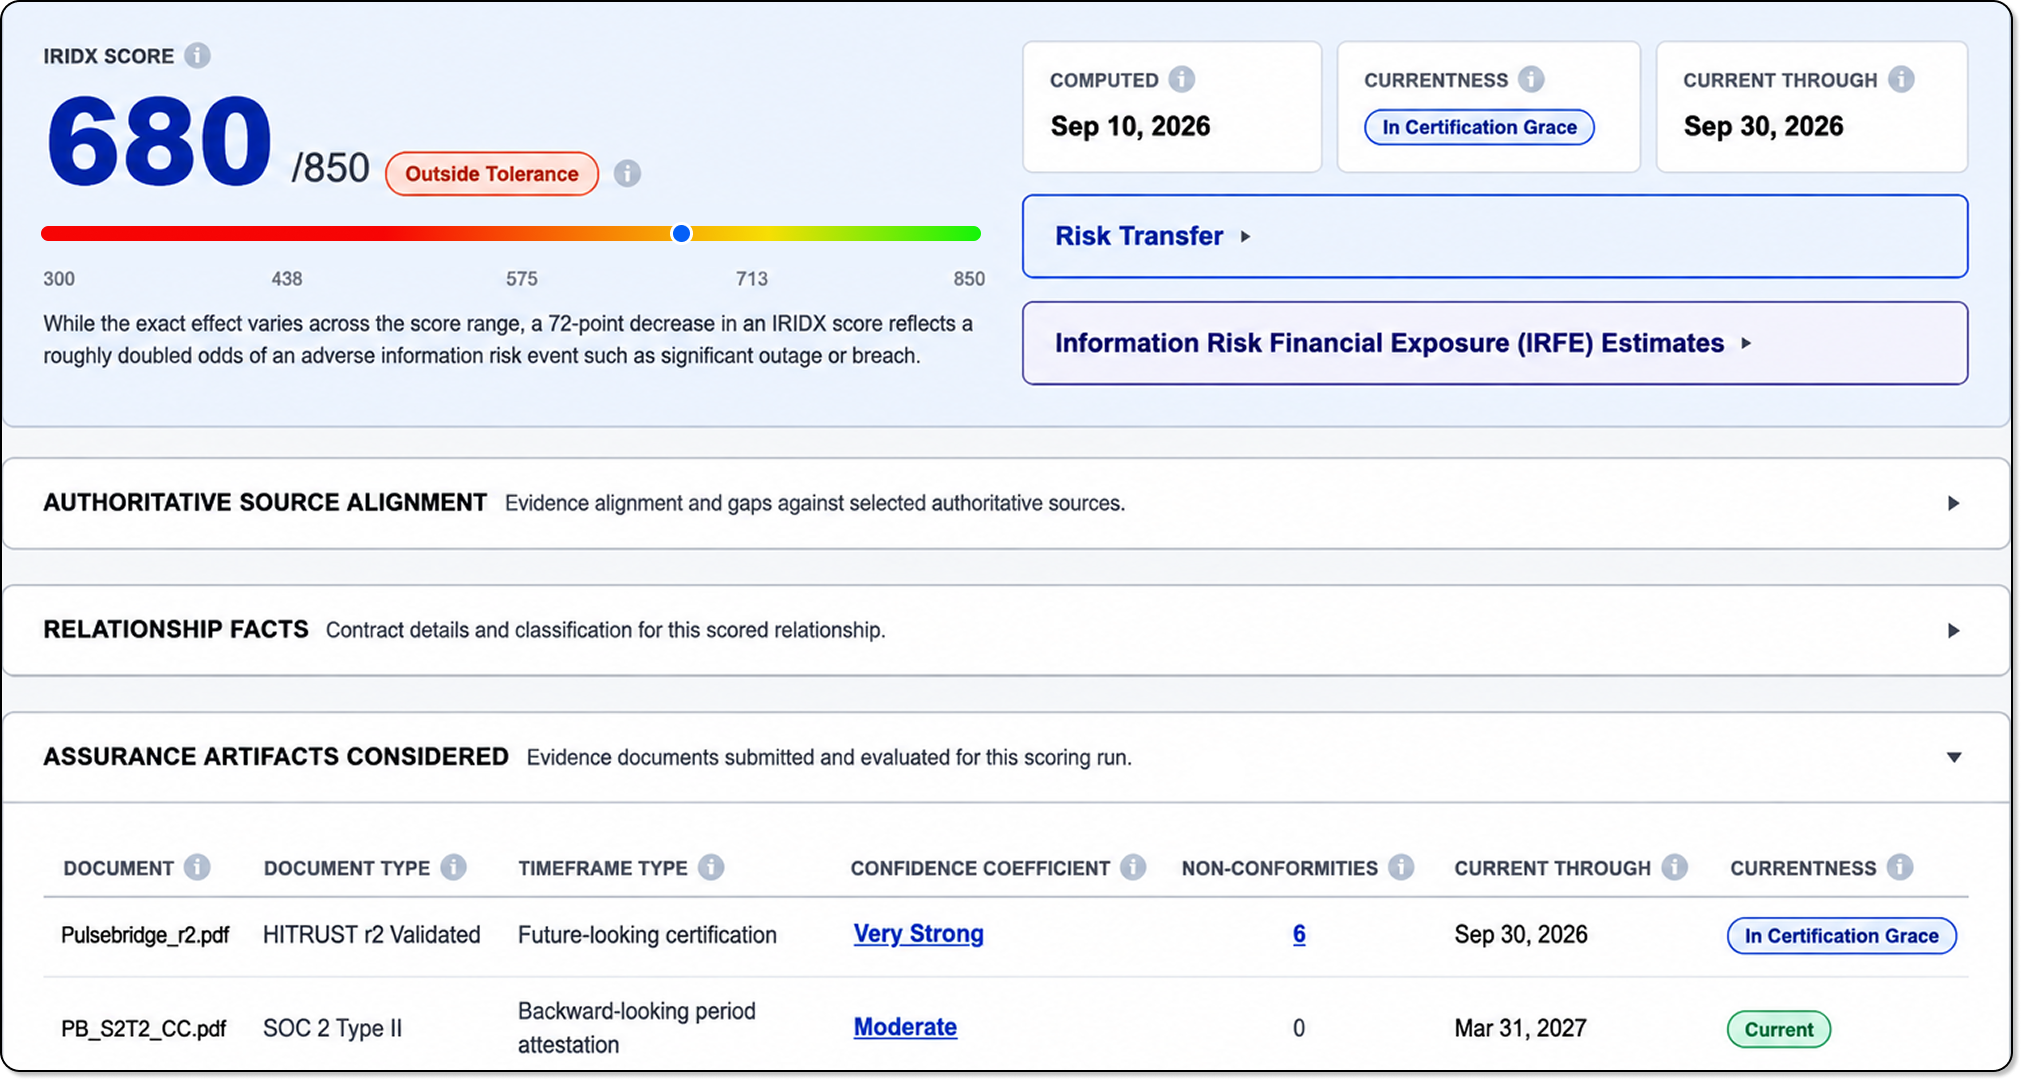
The IRIDX Score
A standardized, explainable measure of residual information risk for a true understanding and enabling precise action.
Turn varied assurance evidence into a standardized, comparable measure of information risk across an entire third-party portfolio.
Add service, contract and business-impact context to estimate the financial exposure associated with a defined third-party relationship.
Compare exposure with approved tolerances, prioritize mitigation, strengthen portfolio oversight and inform decisions to reduce, retain or transfer risk.
IRIDX differentiators
Evaluates the assurance evidence you already have, establishes how well it fits the decision, and how much confidence it deserves.
Uses stable, explainable methods for residual information risk and financial exposure, supporting comparability across relationships and over time.
Govern, manage, and treat risks with precision. Streamline the transfer of third-party information risk outside of tolerance.
See and govern the entire vendor portfolio. Enables TPRM programs to scale to reveal trends, exceptions, concentrations, and financial exposure.
Draws on nearly two decades of control framework and assurance experience, knowledge, and expertise.
IRIDX integrates into your existing processes and takes advantage of the assurance sources you already rely on.
Who it’s for
Third-Party Risk Management Teams
Use available assessments, certifications, and structured questionnaires as the starting point for a more consistent review. Evolve and expand your assurance approach.
Security and Risk Leaders
Move from reviewer-by-reviewer interpretation to a consistent basis for evaluating relationships, setting thresholds, and escalating exceptions.
Business Leaders and Boards
Bring financial context into decisions about accepting, improving, retaining, or transferring third-party information risk.
Risk treatment
True Transfer is a relationship-specific insurance product from Trium Cyber that leverages IRIDX to cover an enterprise’s losses from a third party’s covered security or privacy event. The enterprise holds the policy, creating dedicated protection around a specified third-party relationship or contract.
Coverage and policy terms are determined by the insurer.
Learn More
Before and after
| The Challenges | The IRIDX Outcomes |
|---|---|
| Human analysis of the same evidence yields different answers. | Vendors compared using a common methodology and score. |
| More reviews creates more work to gain more insights. | Targets the gaps that impact decisions. |
| Qualitative risk without financial context. | Understand financial exposure specific to your organization. |
| Boards see activity, not exposure. | Govern tolerance, exceptions, and actions. |
Proof point
“The challenge with vendor management today is that we only get a quantitative view of the number of vendors we’ve reviewed. This isn’t enough in the current threat landscape. We need to understand the risk we’re accepting, where it’s concentrated, and whether we’re within the thresholds we’ve set. We also need to understand the financial exposure of a vendor portfolio and a solution that helps us decide where to reduce risk and how much we’re prepared to retain and how much we need to transfer.”
See how IRIDX can help your organization understand third-party information risk, determine financial exposure, and make decisions with a consistent measurement foundation.
Request a Demo